Remote access, SASE and Zero Trust
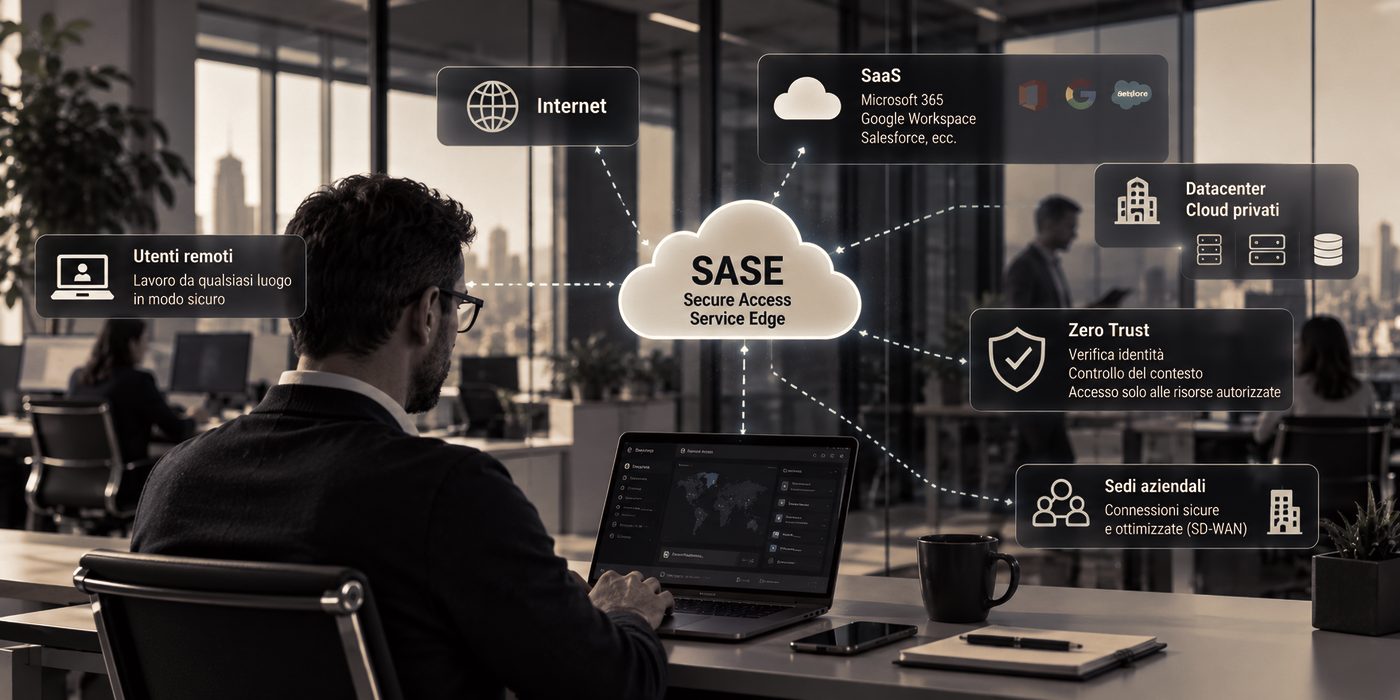
Every user and every device is verified before accessing applications, from anywhere and on any network: for remote workers, branch offices and suppliers.
What the service includes
The perimeter no longer coincides with the office. The Zero Trust model shifts control to the identity, the device and the context of each individual access request.
- ZTNA. Access only to authorised applications, not to the entire network, with continuous verification of user and device.
- SASE. Network security delivered from the cloud for offices and remote users: web filtering, threat protection, control of SaaS applications.
- VPN. Secure remote access with multi-factor authentication and device posture checks.
- Supplier and third-party access. Temporary, limited and tracked access for maintenance engineers and consultants, with session recording.
- Remote working. The same protection as in the office wherever you connect, without burdening the user experience.
How we work
The same four-phase method we apply to every project, adapted to this area.
01
Assess
Survey of current applications, users and access methods, and identification of the most urgent risks.
02
Design
Definition of access policies by role, device and context, and of the migration path from traditional VPN.
03
Implement
Gradual rollout by user and application groups, with testing and training.
04
Operate
Access monitoring, periodic review of permissions and handling of anomalies with the SOC.
Technologies
- Fortinet: FortiSASE, FortiClient and ZTNA
- Cisco: ISE for authentication and access control
- Integration with the corporate identity and multi-factor authentication
Want to secure your remote access?
Tell us about your situation: we will reply with a concrete proposal. You can also call us on 800 035 430.