Compliance, VA and PT
From gap analysis to the measures required by NIS2, with periodic testing that measures the real effectiveness of your defences.
What the service includes
Compliance shows that you have done things properly; testing shows that they work. The two paths reinforce each other.
- NIS2 gap analysis. Comparison of existing measures against the requirements of Italian Legislative Decree 138/2024, with priorities and a remediation plan.
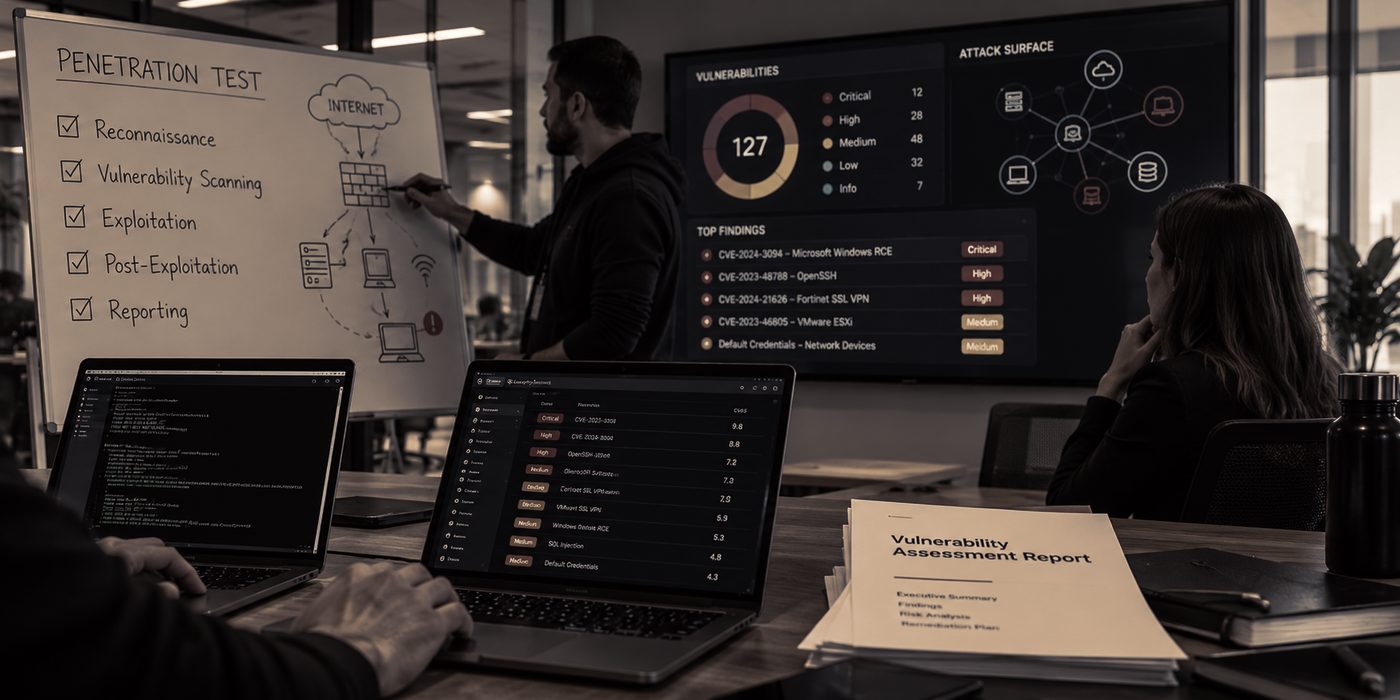
- Vulnerability Assessment. Periodic scanning of network, servers and applications, with vulnerabilities classified by real risk.
- Penetration Test. Simulated attack by specialists, covering the external perimeter, the internal network and web applications.
- Report and remediation. Results that are readable by both management and technical staff, with practical guidance on how to fix issues.
- Ongoing management. Tests repeated after fixes and at regular intervals, to keep risk under control over time.
How we work
The same four-phase method we apply to every project, adapted to this area.
01
Assess
Definition of scope, objectives and rules of engagement, also in relation to regulatory obligations.
02
Design
Planning of tests and analysis activities, with agreed time windows to minimise the impact on operations.
03
Implement
Execution of the checks and delivery of a report with evidence and priorities.
04
Operate
Support with remediation, retesting and integration with the SOC’s vulnerability management.
References
- NIS2 – D.Lgs. 138/2024
- GDPR
- National Cybersecurity Framework
- ISO/IEC 27001
Want to know where you stand with NIS2?
Tell us about your situation: we will reply with a concrete proposal. You can also call us on 800 035 430.