CRA and Machinery Regulation
For manufacturers of machinery and products with digital elements: requirements analysis, risk assessment, technical documentation and secure development lifecycle, through to vulnerability management after placement on the market.
What the service includes
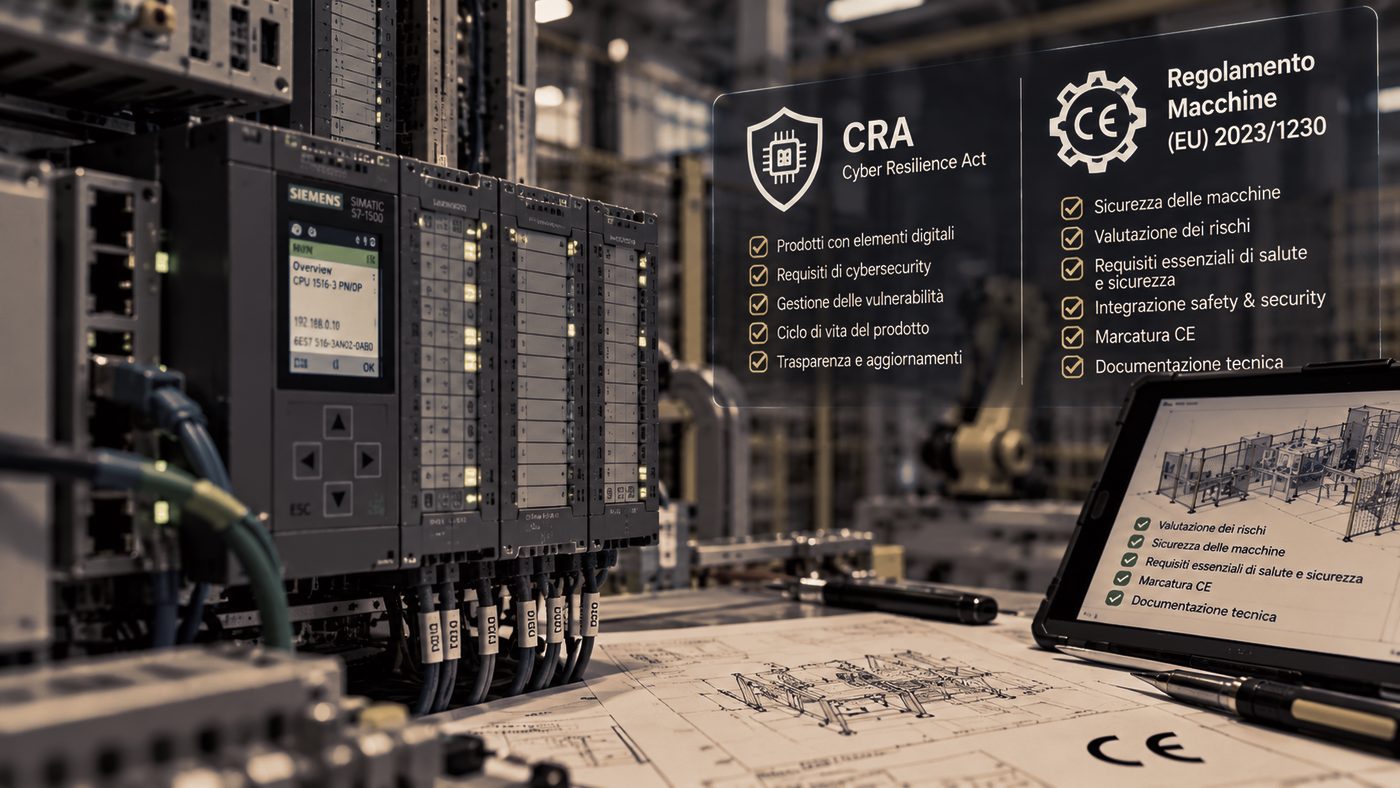
For manufacturers, cyber security becomes a product requirement, to be demonstrated in order to obtain CE marking. Two European regulations make this explicit.
- Cyber Resilience Act. Regulation (EU) 2024/2847 for products with digital elements. Reporting obligations for actively exploited vulnerabilities apply from 11 September 2026, the main obligations from 11 December 2027.
- Machinery Regulation. Regulation (EU) 2023/1230, applicable from 20 January 2027, with requirements on protection against tampering and corruption of the control system.
- Requirements and risk analysis. Product classification, applicable requirements and cyber security risk assessment.
- Technical documentation. Preparation of the documents supporting the conformity assessment.
- Secure development lifecycle. Design, testing and update processes according to IEC 62443-4-1 and component requirements according to 4-2.
- Vulnerability management. Collection of reports, assessment, remediation and communication to users after placement on the market.
How we work
The same four-phase method we apply to every project, adapted to this area.
01
Assess
Analysis of the product, the applicable legislation and the current state of development processes.
02
Design
Compliance plan, with security requirements built into the design and the development lifecycle.
03
Implement
Implementation of measures on the product and drafting of the technical documentation.
04
Operate
Management of vulnerabilities and updates throughout the product lifecycle.
References
- Regulation (EU) 2024/2847 – Cyber Resilience Act
- Regulation (EU) 2023/1230 – Machinery
- IEC 62443-4-1 – Secure product development lifecycle
- IEC 62443-4-2 – Technical requirements for components
Learn more
Want to prepare your products for the new rules?
Tell us about your situation: we will reply with a concrete proposal. You can also call us on 800 035 430.